Installing and Setting up the Checkmarx Cursor Extension
Installing the Extension
The Cursor Extension is available on the Open VSX Registry. You can initiate the installation directly from within Cursor.
Notice
Although there is no dedicated Checkmarx plugin for Cursor, the plugin for VS Code has been tested and is effective for use in Cursor.
Warning
The Checkmarx VS Code extension includes the Checkmarx One Assist feature as part of the Checkmarx One platform experience and should be used by Checkmarx One customers with a Checkmarx One Assist license. The Checkmarx and Checkmarx Developer Assist VS Code extensions are mutually exclusive. To use the Checkmarx extension, ensure that the Checkmarx Developer Assist extension is uninstalled before installation. If you are not a Checkmarx One customer and are trying to install the Checkmarx Developer Assist VS Code extension, see Initial Setup and Configuration.
To install the extension:
Open Cursor.
In the main menu, click on the Extensions icon.
Search for the Checkmarx extension, then click Install for that extension.
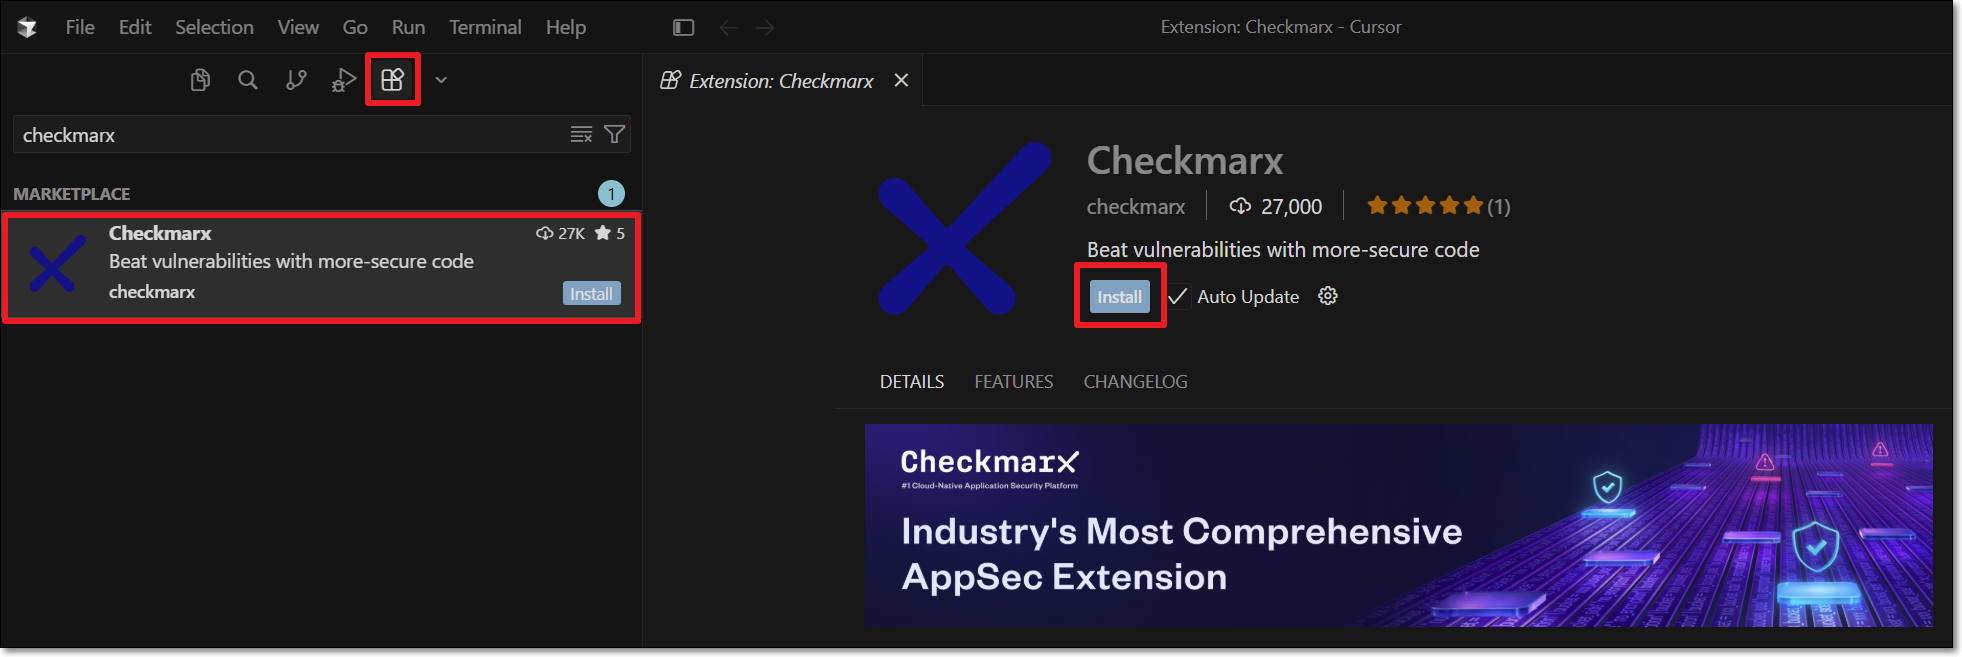
The Checkmarx extension is installed.
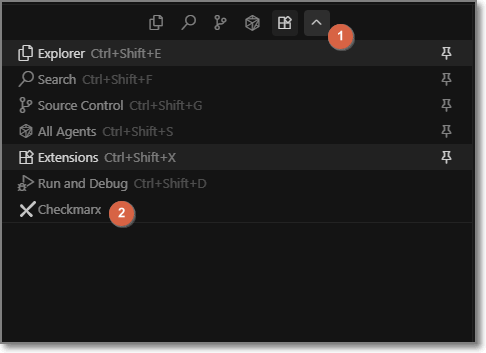
To open the Checkmarx extension, click the arrow box next to the extension icon, and select the Checkmarx icon.
Setting up the Extension
After installing the plugin, in order to use the Checkmarx One Platform tool you need to configure access to your Checkmarx One account, as described below.
Notice
If you are only using the free KICS Auto Scanning tool and/or the SCA Realtime Scanning tool, then this setup procedure is not relevant. However, for SCA Realtime Scanning tool, if your environment doesn't have access to the internet, then you will need to configure a proxy server in the Settings, under Checkmarx One: Additional Params.
In the Cursor console, click on the Checkmarx extension icon.
The Checkmarx One Authentication sidebar opens:
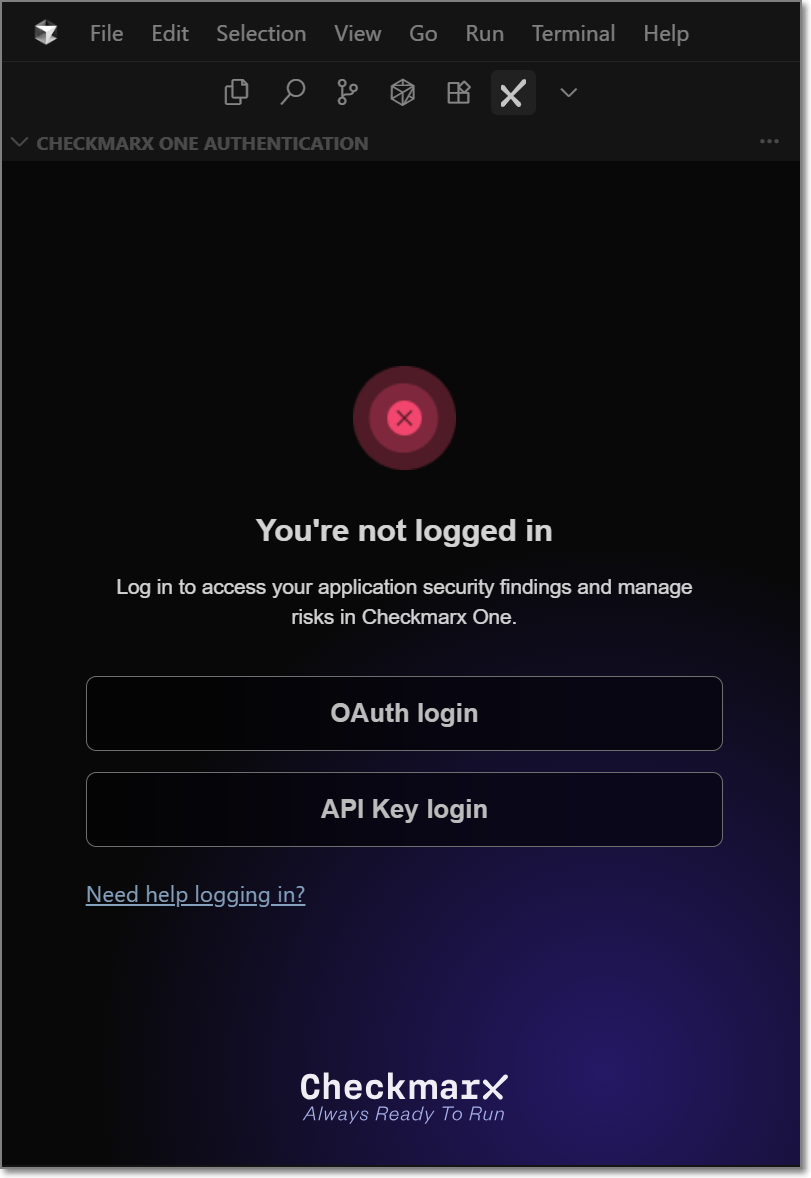
In the Checkmarx One Authentication sidebar, connect to Checkmarx One either using an API Key or login credentials.
Important
In order to use this integration for running an end-to-end flow of scanning a project and viewing results with the minimum required permissions, the API Key or user account should have the Checkmarx One
plugin-scannerrole and the IAMdefault-roles<tenant>role.The permissions included in
plugin-scannerare shown here. If you would like to create a custom role with more granular permissions, you should refer to this list of permissions in order to determine which permissions you will need to assign.Login Credentials
Select the OAuth login button.
The OAuth Log in window opens.
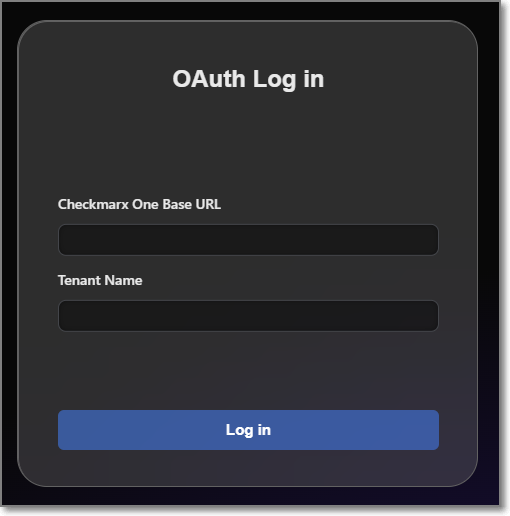
Enter the Base URL of your Checkmarx One environment and the name of your tenant account, then click Log in.
Notice
Once you have submitted a base URL and tenant name, it is saved in cache and can be selected for future use (saves up to 10 accounts).
A confirmation dialog asks for permission to open an external website.
Click on Open to proceed.
Notice
If you would like to prevent this dialog from opening in the future, click on Configure Trusted Domains and then in the Command Pallete click on Trust....
If you are logged in to your account, the system connects automatically. If you are not logged in, your account's login page opens in your browser. Enter your Username and Password and then your One-Time Password (2FA) to log in.
API Key (see Generating an API Key)
Select the API Key login button.
The API Key Log in window opens.
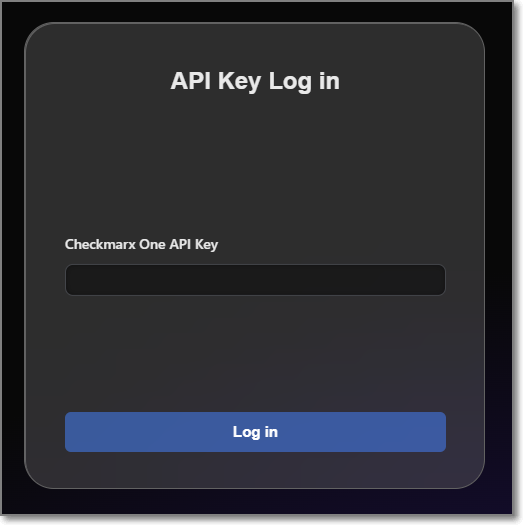
Enter your Checkmarx One API Key and click Log in.
The Checkmarx One Authentication sidebar will now show that you are logged in.
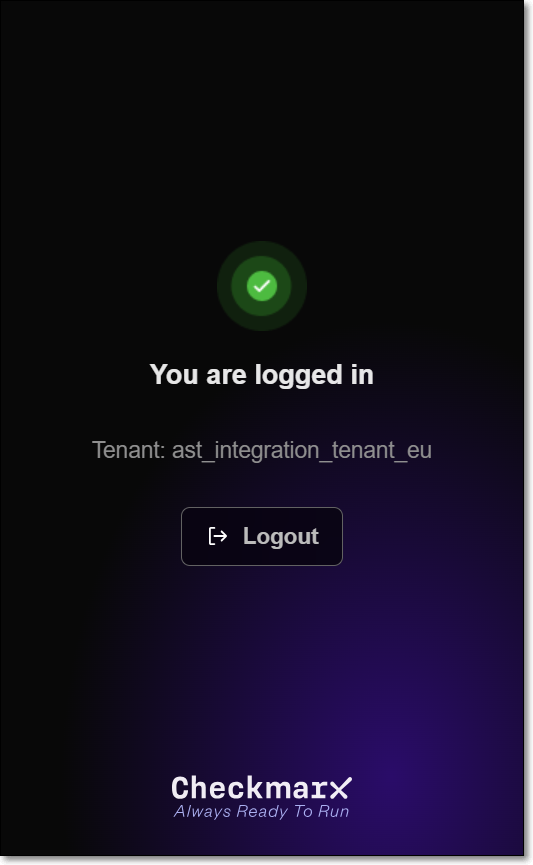
A Checkmarx welcome page is displayed immediately after a successful login.
At the top right of the Checkmarx One Authentication sidebar, select the more options icon and click Settings.
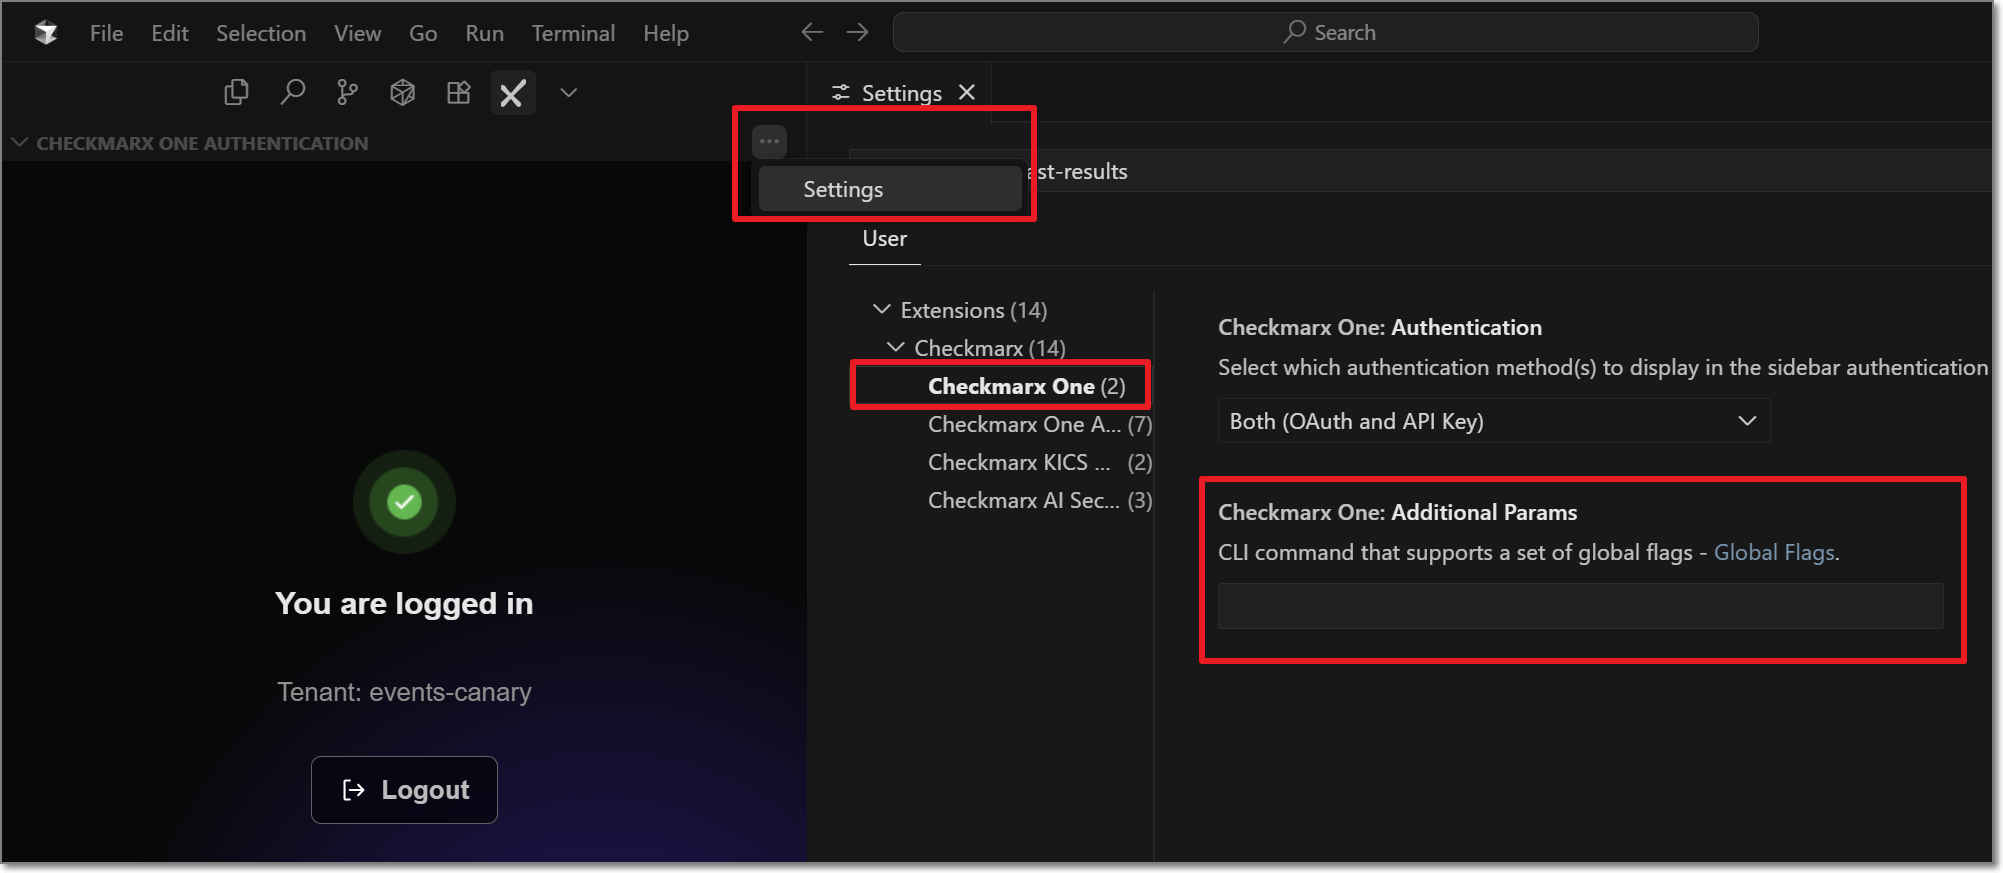
Navigate to the Checkmarx One settings tab, and in the Additional Params field, you can submit additional CLI params. This can be used to manually submit the base url and tenant name if there is a problem extracting them from the API Key. It can also be used to add global params such as
--debugor--proxy. To learn more about CLI globalparams, see Global Flags.
Configuring Checkmarx Developer Assist
By default, Developer Assist uses the native Cursor AI Assistant and OAuth to authenticate the Checkmarx MCP server. If you keep these defaults, you only need to complete Default Setup below.
If you use a different AI Assistant or authentication method, use the table to find the steps that apply to you.
AI Assistant | MCP Authentication | What to do |
|---|---|---|
Native Cursor (default) | OAuth (default) | |
Codex or Claude | OAuth | Changing the Defaults and then Authenticating with Codex or Claude |
Any | Token Based |
Default Setup: Cursor Assistant with OAuth
Open Cursor Settings and under Customize > MCP, click Connect in the Checkmarx row.
When prompted, allow Cursor to open the Checkmarx web application and complete the authentication process.
Changing the Defaults
Follow these steps only if you want to use an AI Assistant other than the native Cursor assistant, or the Token Based authentication method.
In the Checkmarx One Results sidebar, click the more options icon and select Settings. Then go to Checkmarx > Checkmarx One Assist.
By default, Prefer Native AI Assistant is selected, and the AI Assistant setting is ignored. To use a different assistant:
Clear Prefer Native AI Assistant.
From the AI Assistant dropdown, select the assistant to use for remediation: Copilot, Claude or Codex.
Warning
If the AI Assistant you select is not installed, the extension falls back to the local IDE assistant.
Under MCP Authentication, select the authentication method used by the Checkmarx MCP server.
OAuth (default) when the MCP server starts, a browser-based login session is initiated to authenticate with your Checkmarx One account.
Token Based uses the API key associated with your current Checkmarx One login and avoids browser authentication when starting the MCP server.
Warning
With Token Based authentication, the API key is stored in plain text in the MCP configuration file. Do not commit or share this file.
Click Install MCP to update the MCP configuration file.
Authenticating with Codex or Claude
If you selected Codex or Claude as the AI Assistant and kept OAuth as the MCP Authentication method, you must authenticate to the Checkmarx MCP server manually from within the assistant. Follow the procedure for your assistant.
Optional scanner settings
You can choose which realtime scanners run and, for IaC scanning, which container tool is used. To adjust these, go to Checkmarx > Checkmarx One Assist settings.
Choose the scanners to run. Select or clear the checkbox for each scanner. If MCP is activated at the tenant level, all scanners are selected by default.
Select the container tool for IaC scanning. If you use the IaC Realtime scanner, select the Containers Management Tool used in your environment: docker or podman.
The extension normally creates and configures the MCP configuration file automatically. Manual configuration is only required if automatic configuration fails or if you prefer to create the MCP configuration yourself. The file and its format depend on your AI Assistant.
Configuring AI Security Champion
AI Security Champion can be used with the Checkmarx One tool as well as with the KICS Realtime Scanning tool. In order to use AI Security Champion you need to integrate the extension with your OpenAI account.
Notice
If the Global Settings for your account have been configured to use Azure AI instead of OpenAI, then the credentials are submitted on the account level and it is not possible to submit credentials in your IDE for an alternative AI model.
To set up the integration with your OpenAI account:
Go to the Checkmarx extension Settings and select Checkmarx AI Security Champion.
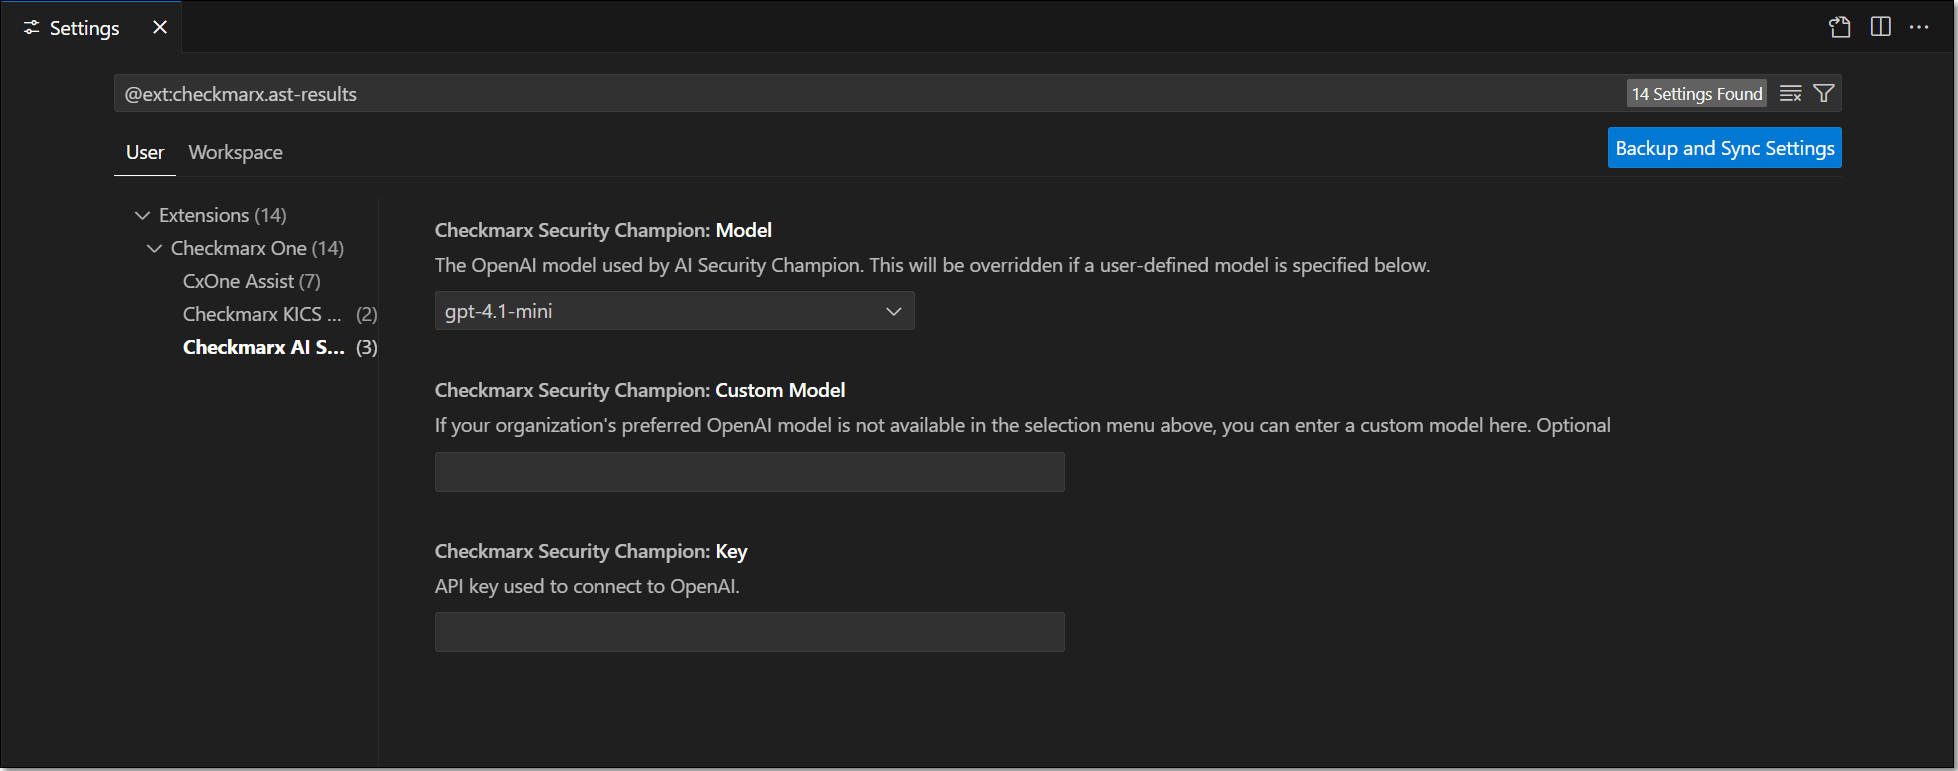
In the Model field, select from the drop-down list the model of the GPT account that you are using.
In the Key field, enter the API key for your OpenAI account.
Notice
Follow this link to generate an API key.
The configuration is saved automatically.
Configuring the KICS Realtime Scanning Tool (Optional)
This tool is activated automatically upon installation and no configuration is required.
Notice
It is not necessary to configure the Checkmarx One Authentication settings in order to use the KICS Realtime Scanning feature.
If you would like to customize the scan settings, you can use the following procedure:
In the VS Code console, go to Settings > Extensions > Checkmarx > Checkmarx KICS Auto Scanning.
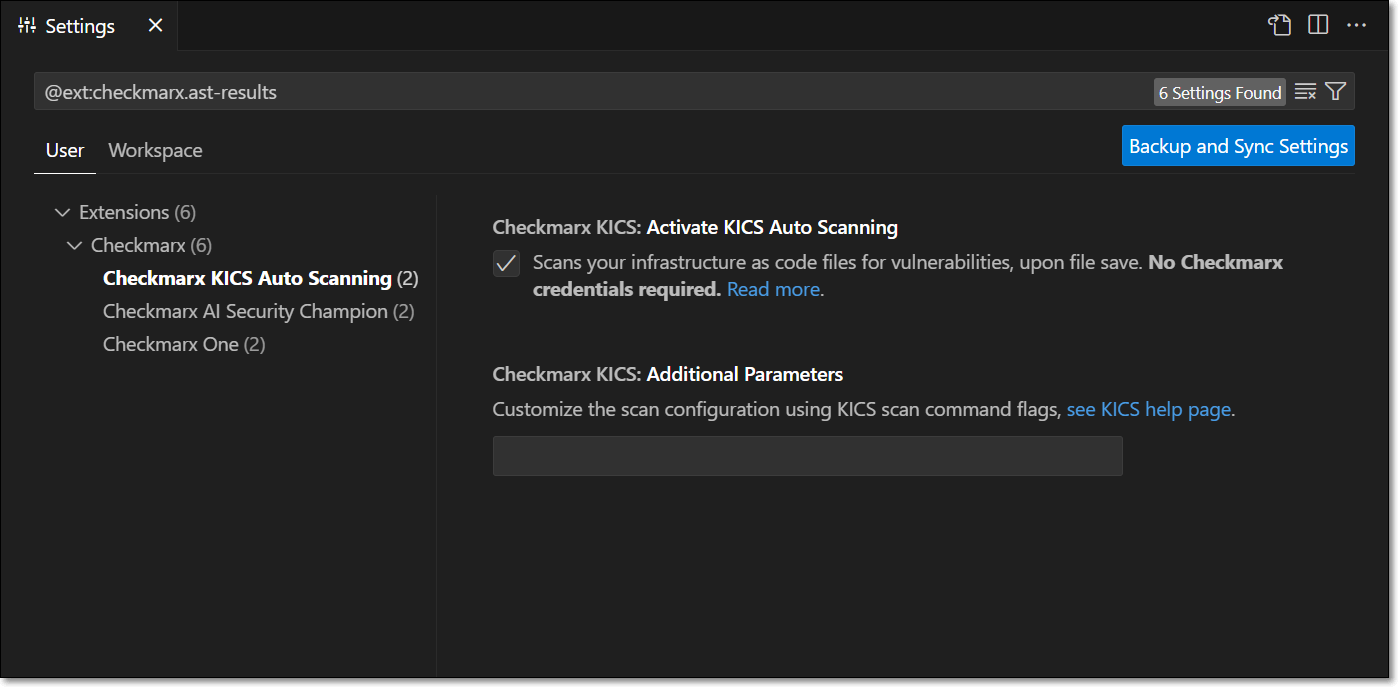
By default the extension is configured to run a KICS scan whenever an infrastructure file of a supported type is opened or saved. If you would like to disable automatic scanning, deselect the Activate KICS Auto Scanning checkbox.
Notice
In this case, you will still be able to trigger scans manually from the command palette.
If you would like to customize the scan parameters, enter the desired flags in the Additional Parameters field. For a list of available options, see Scan Command Options.